Managed security services
Your outsourced security team — without the cost of building one
BTInfosec monitors, tests and hardens the systems your business runs on — then hands you the evidence your board, your auditor and your regulator expect. One predictable monthly fee.
NDPA-aligned reporting · ISO/IEC 27001:2022 · CBN framework aware · PCI DSS v4.0
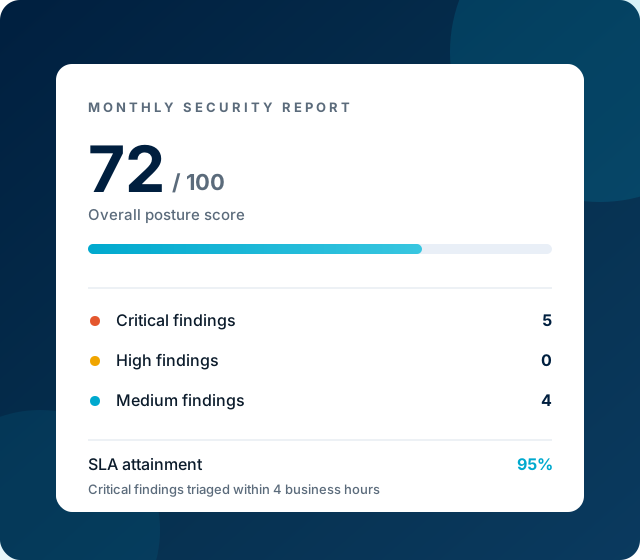
≤ 4 business hours
Critical findings triaged and explained
≤ 15 minutes
Acknowledgement of critical detection alerts
7 days
Target remediation window for critical findings
Every month
Board-ready report with trend and SLA attainment
What we do
Six services that replace a security team you can’t hire
Start with the one that hurts most, or take the full managed programme. Every service comes with named deliverables, a named owner and a timetable.
Vulnerability management
Continuous scanning, exploitability-based triage and a remediation register tracked to closure every month.
Detection & response
Alert triage and escalation on your estate, so a real attack is separated from noise and handed to a human fast.
Assurance & testing
Penetration testing, web application testing and cloud configuration review, with findings you can actually action.
GRC & compliance
NDPA and NDPC readiness, ISO/IEC 27001:2022 gap analysis and a policy set your auditor will accept.
Security awareness
Phishing simulation, staff training and reporting that shows whether your people are actually getting safer.
Fractional CISO
A senior security owner for your roadmap, board reporting and regulator conversations, part-time.
Why BTInfosec
Enterprise-grade security, priced for a mid-market budget
You do not need a full security department. You need someone accountable for the work, a timetable you can hold them to, and proof you can hand to a regulator.
- Named owner and named SLA on every finding — no “we’ll look into it”.
- Findings scored by real exploitability, not raw scanner severity, so you fix what matters first.
- Reports written for a board, an auditor and a regulator — not a wall of technical noise.
- Remediation tracked to closure, with the evidence trail kept for you.
- Local team, local timezone, and a price set for Nigerian operating budgets.
“Most breaches we are called into were visible for weeks in a scan nobody read. Our job is to make sure that report gets read, owned and closed.”
BTInfosec delivery team
- Triage in 4 business hours, not 4 weeks
- Escalation paths your team can actually reach
- Exit plan agreed before you sign
Compliance
Evidence the frameworks your regulator and your customers care about
We map your controls and your findings to the standard you are being measured against, and produce the paperwork that shows where you stand — including the gaps you have not closed yet.
Built for the sectors that carry the most risk
How we work
A rhythm you can hold us to, every month
01 — ASSESS
Free posture assessment
We look at your external footprint and the risks you already know about, and give you a scored report you keep.
02 — PRIORITISE
Fix what actually matters
Findings are re-scored for exploitability and asset criticality, so a noisy scanner list becomes a short, ordered plan.
03 — OPERATE
Monitoring and remediation
We keep scanning, watch for detection alerts and track every finding to closure with a named owner and a deadline.
04 — PROVE
Report, review, renew
A monthly report for your board and a quarterly review of the programme, so the value of the retainer stays visible.
Managed service tiers
One predictable monthly fee
Annual commitment, billed monthly, with a one-off onboarding fee that funds the deployment work. Indicative pricing — final scope confirmed after your assessment.
Essential
For companies that need to see and close their vulnerabilities.
₦1.2m / month
- Continuous vulnerability management
- Monthly scan of the agreed estate
- Exploitability-based triage
- Remediation register to closure
- Monthly board-ready report
- Security awareness subscription
Most popular
Standard
The managed security programme most clients start on.
₦2.2m / month
- Everything in Essential
- Detection & response (MDR-lite)
- Alert triage and escalation
- GRC and compliance support
- Quarterly business review
- Priority support
Pro
For regulated businesses that need a security owner at the table.
₦3.4m / month
- Everything in Standard
- Fractional CISO
- Compliance programme ownership
- Incident response retainer
- 24/7 critical escalation
- Regulator and board engagement
Free · no obligation
Start with a free Security Posture Assessment
A bounded, fixed-scope review that tells you where you stand — and what a regulator or a customer’s due-diligence questionnaire would find.
- A scored assessment report you keep, whether or not you engage us
- The compliance gaps we can see from outside your network
- A prioritised list of what to fix first, and roughly what it costs
- A clear recommendation on tier and scope — no hard sell
Ready to stop guessing about your security posture?
Book a free assessment, or call the team on +234 815 213 5909. Managed clients get 24/7 escalation on critical alerts.